Know your
attack surface
Our cybersecurity experts combine hands-on testing with in-house AI tools to deliver industry-leading cybersecurity services. With a special focus on HIPAA compliance, we identify risks to electronic patient information and show you what to fix first.
Security services
See what’s exposed, test the defenses around it, and give the people responsible a clear order for repairs.
Open-source intelligence (OSINT)
Find forgotten domains, exposed documents, and sites that imitate your brand. See the public evidence behind each finding.
Penetration testing
Test network and application defenses under agreed rules. Learn which weaknesses matter to your operations and how to verify a fix.
Risk assessments
Rank risks to critical systems and suppliers. For HIPAA compliance work, document gaps in safeguards for electronic protected health information.
Reverse engineering
Learn what an unfamiliar file actually does and give responders evidence they can use to decide what to contain.
Threat management
Use threat intelligence to decide what to monitor, which alerts need attention, and who takes the next step.
Processes & procedures
Create or revise security policies and playbooks so staff know what to do, who approves it, and what evidence to keep.
Our approach
From scope to remediation
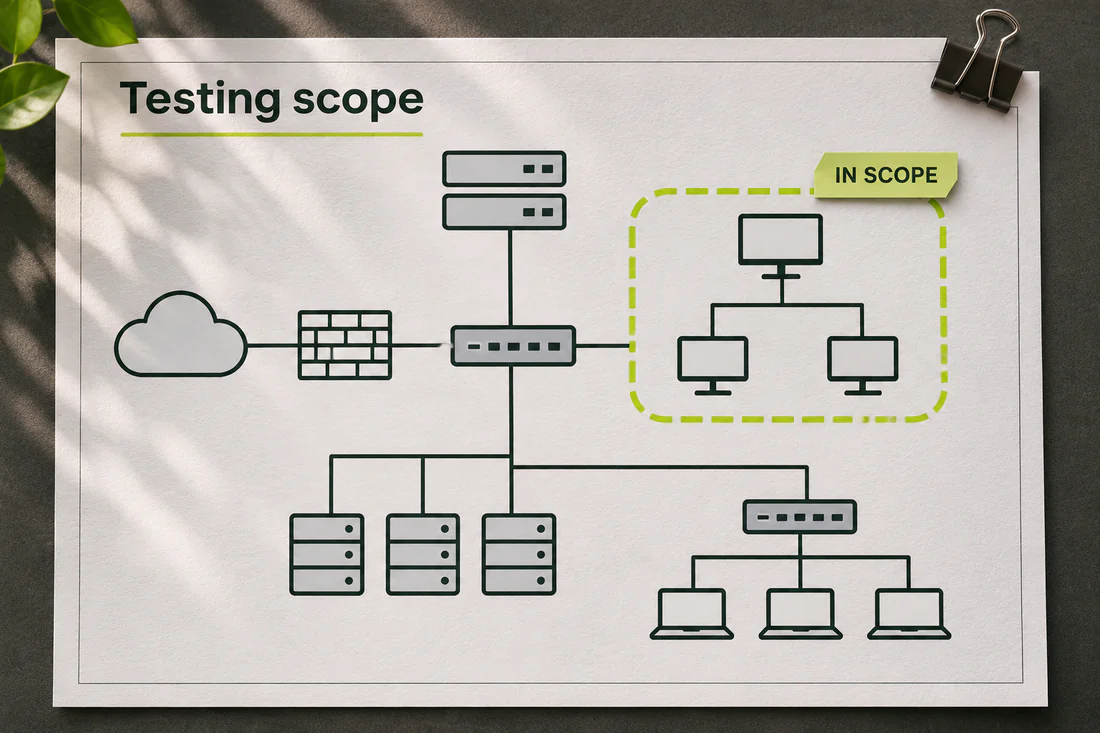
Define the scope
The scope defines what we have permission to test and why. Together we identify the target applications, networks, or cloud systems and agree in writing on exclusions, permitted methods, and testing windows.
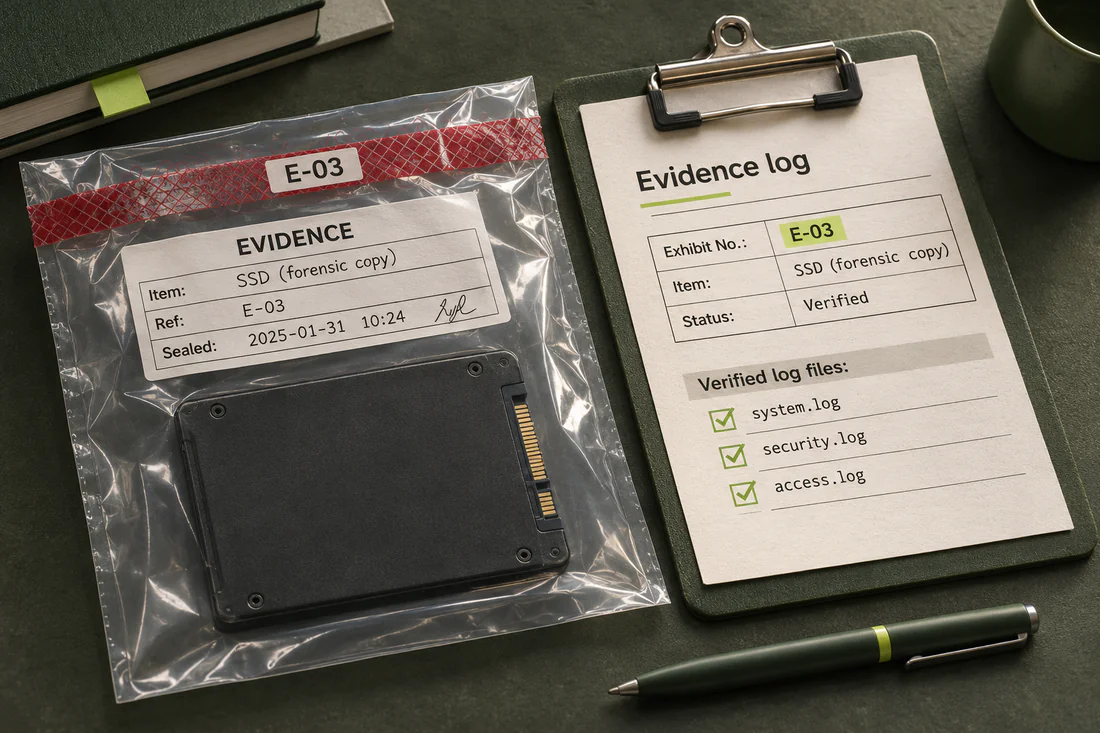
Gather and verify evidence
We collect system inventories, configurations, and logs. Our in-house AI agent helps analysts spot patterns in scan results and threat reports. Analysts check those leads against source records and confirm the context with your team.
Perform authorized testing
Our consultants run vulnerability scans and conduct hands-on penetration tests within the agreed scope. We test safeguards such as account permissions and network segmentation to determine which weaknesses could expose data or interrupt operations.
Report the findings
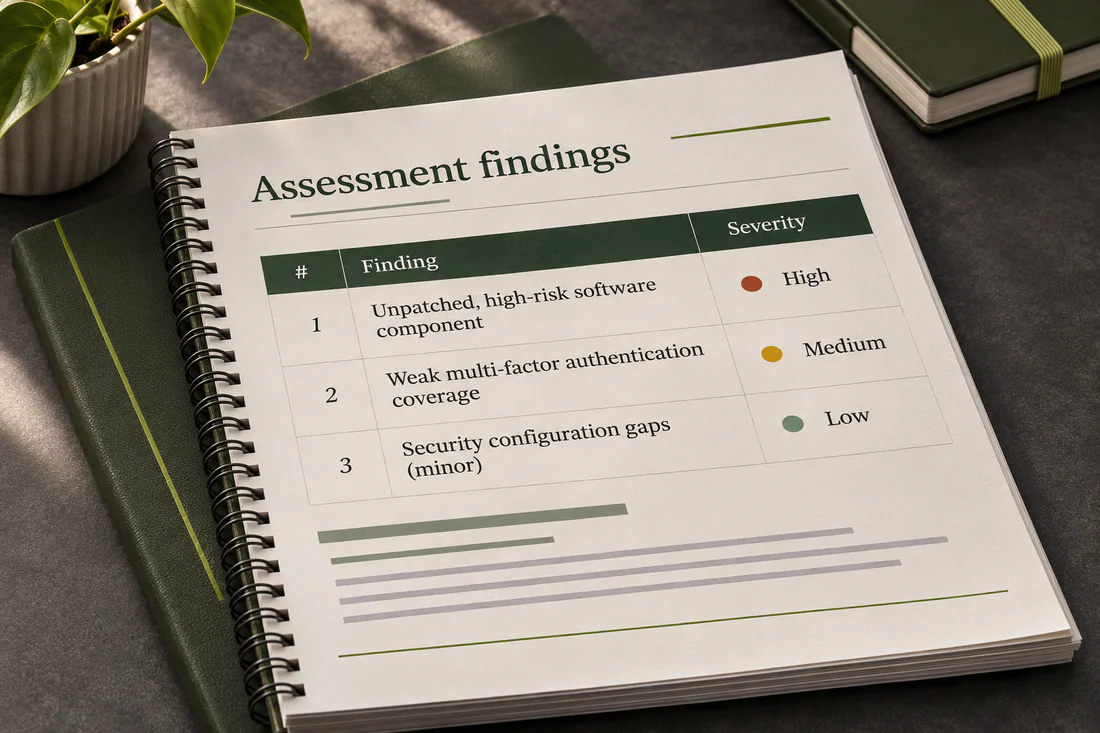
You receive an executive summary and a technical report. Each finding identifies the affected systems, supporting evidence, severity, and business impact. For audits, we map evidence to the requirements under review. A HIPAA assessment might show that a clinic’s logs do not identify who opened a patient record.
Plan the fixes
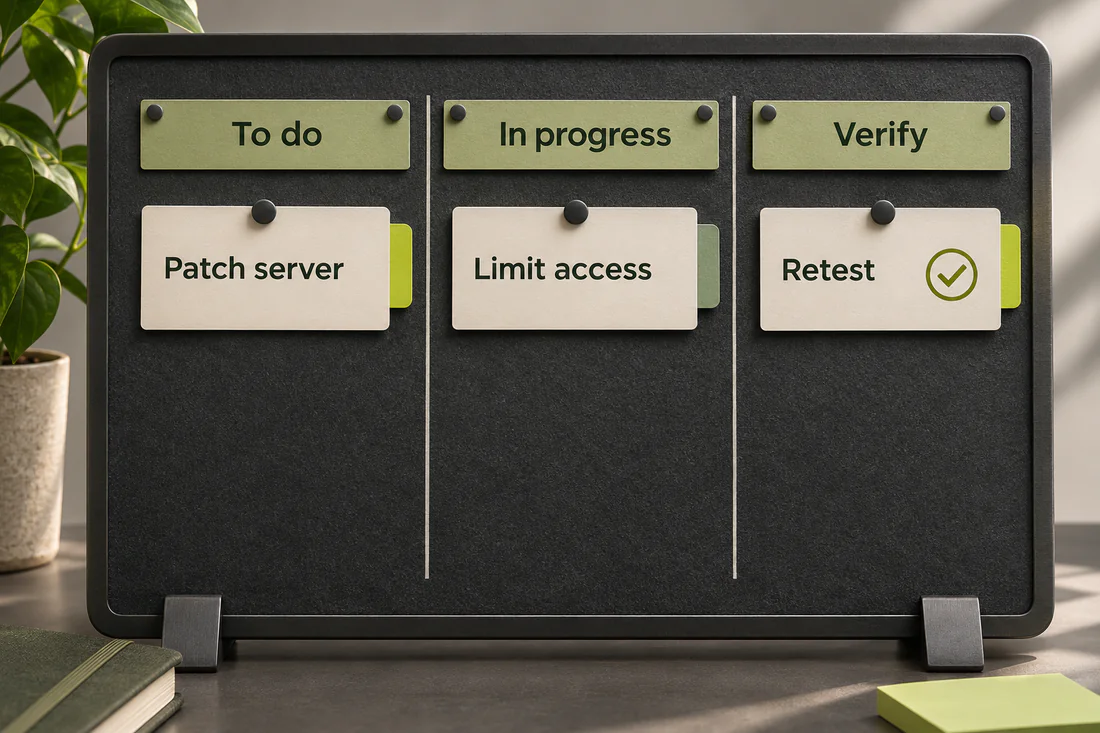
We help your team prioritize fixes such as software patches, access changes, and revised procedures. Each action gets an owner, a target date, and a way to verify it. We retest agreed fixes and document any remaining risk.
White Beret Security Solutions, LLC
Why the white beret?
Our name is a nod to the white-hat hacker who investigates weaknesses with the owner’s permission. That principle shapes how we agree on scope, handle evidence, and brief the people responsible for fixing a problem.
About the firmWhat do you need to secure?
Tell us what’s changing in your business or which security question you need answered.